Continuous Agentic Pentesting
Security that evolves with every release
Traditional pentests provide a snapshot. Once the report is in, your code has already changed, and new risks emerge.
Woolves makes security continuous. With Continuous Agentic Pentesting, testing becomes a structural part of your development cycle. No waiting times, no separate projects, but a rhythm of testing, improving, and validating.
> This is how it works
Why Continuous Agentic Pentesting
One-off pentests provide a snapshot. But vulnerabilities don’t appear once a year — they emerge with every sprint, release and integration.
Continuous Agentic Pentesting keeps your attack surface in view every day, and tests it in depth with every Agentic Pentest.
Ongoing. Proactive. Structured.
- Ethical hackers aligned with your development rhythm
- Vulnerability testing for every release or request
- Retests in the Woolves Portal
- Threat modeling for what’s next — not just what’s live
Not a report. A relationship.
> This is how it works
Getting
started
with
Continuous Agentic Pentesting
Digital intake
White, grey, or black box. For web apps, APIs, or complete platforms. Our community tests what you build — as often as you need.
Define your intensity
Whether you need dedicated pentesting hours each month or continuous scanning at the frequency you choose — the pack adapts to your environment.
Woolves activated
Once you implement a solution, hackers will test again. What is fixed, stays fixed.
Make it safe
New releases are automatically included. This creates an ecosystem where security grows with your product: proactive security instead of reactive control.
Retest
Every finding appears directly in the Woolves platform. Clear, structured, including impact, risk, and reproduction instructions.
Report
Once you implement a solution, hackers will test again. What is fixed, stays fixed.

Woolves platform
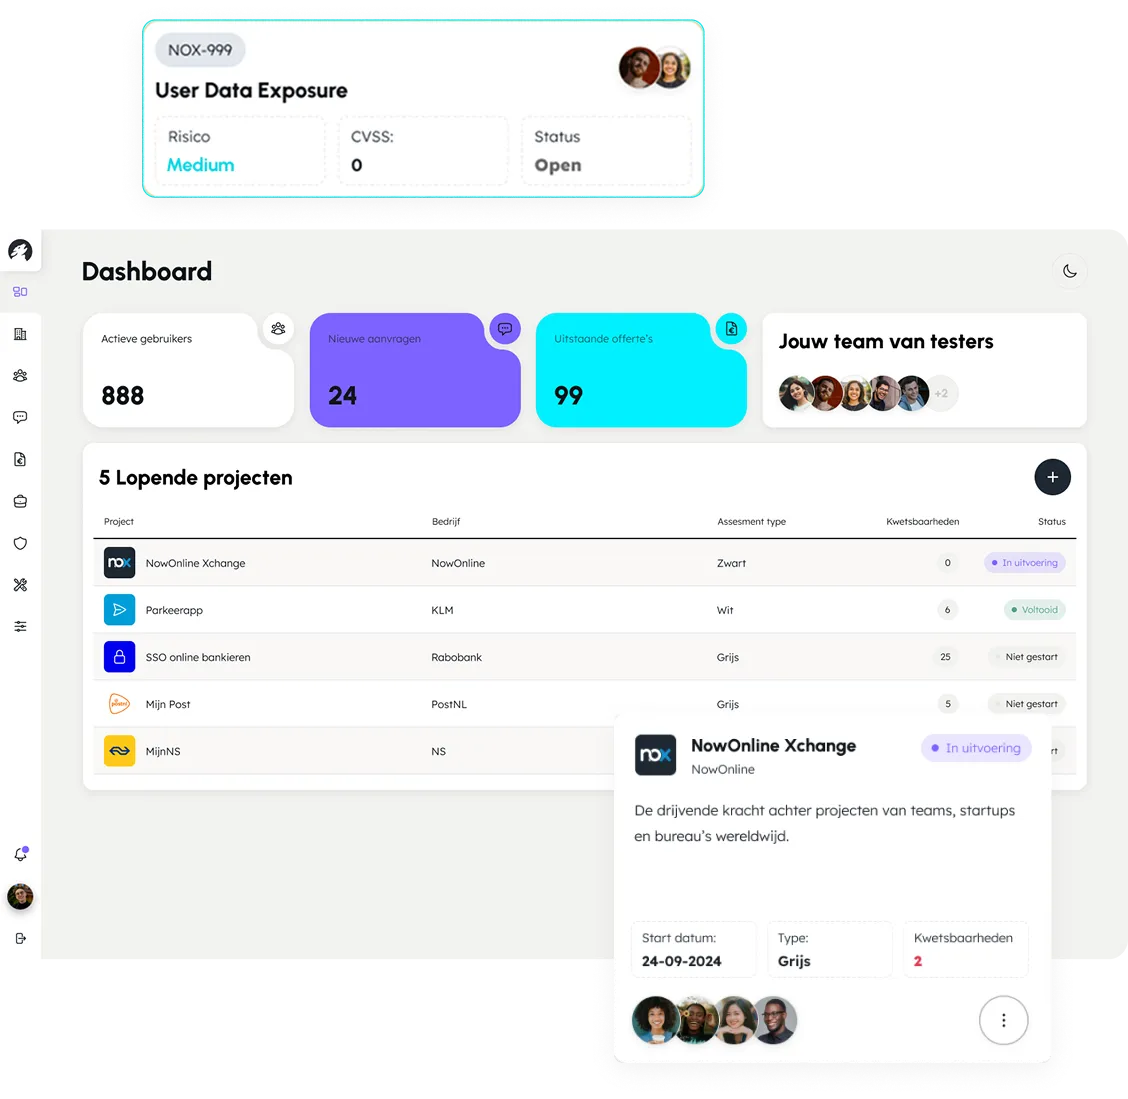
From insight to action, in one place
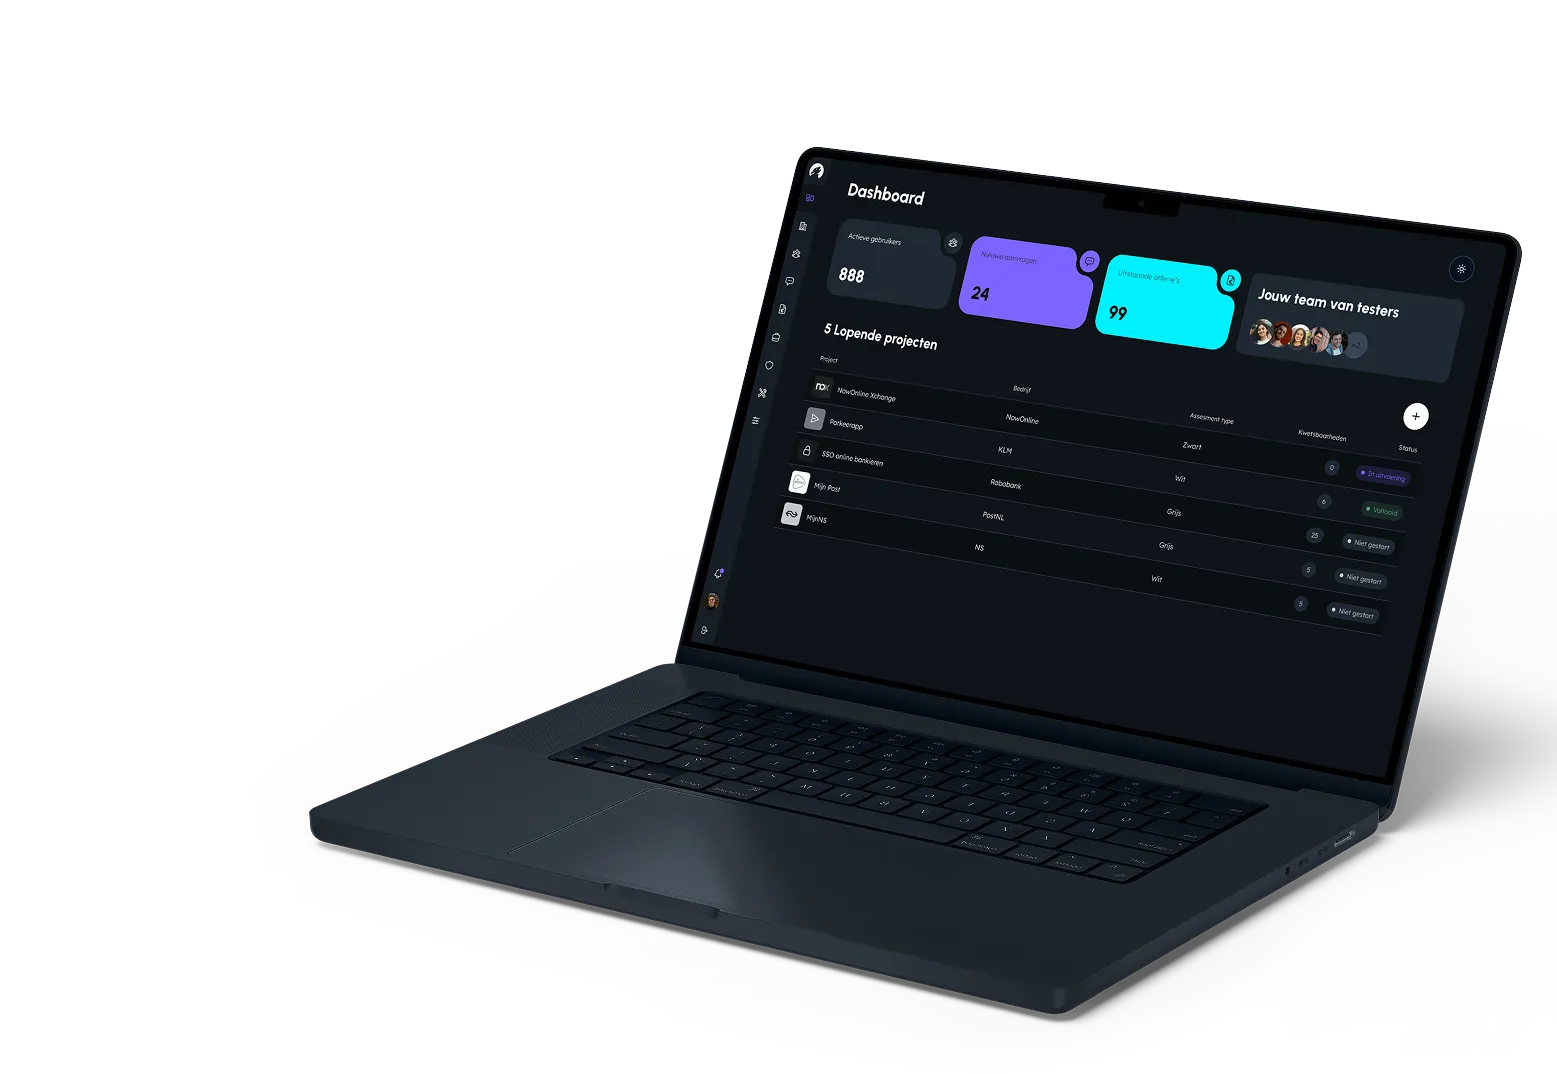
The Woolves platform brings testing, reporting, and learning together in one place.
Findings appear instantly in a clear interface that fits your development workflow. Issues, priorities, and fixes sit side by side, so teams move faster and keep knowledge where it belongs.
These organizations have already been hacked by us
Organizations across various sectors work with Woolves to reduce their digital risk.
>_ get started now
Predator precision,
protector mindset
protector mindset
Choose a plan that fits your needs, from an initial check to continuous security.

>_ schedule a demo
Make your software safer and your team stronger
Schedule a demo and see how continuous security becomes a natural part of your development process.